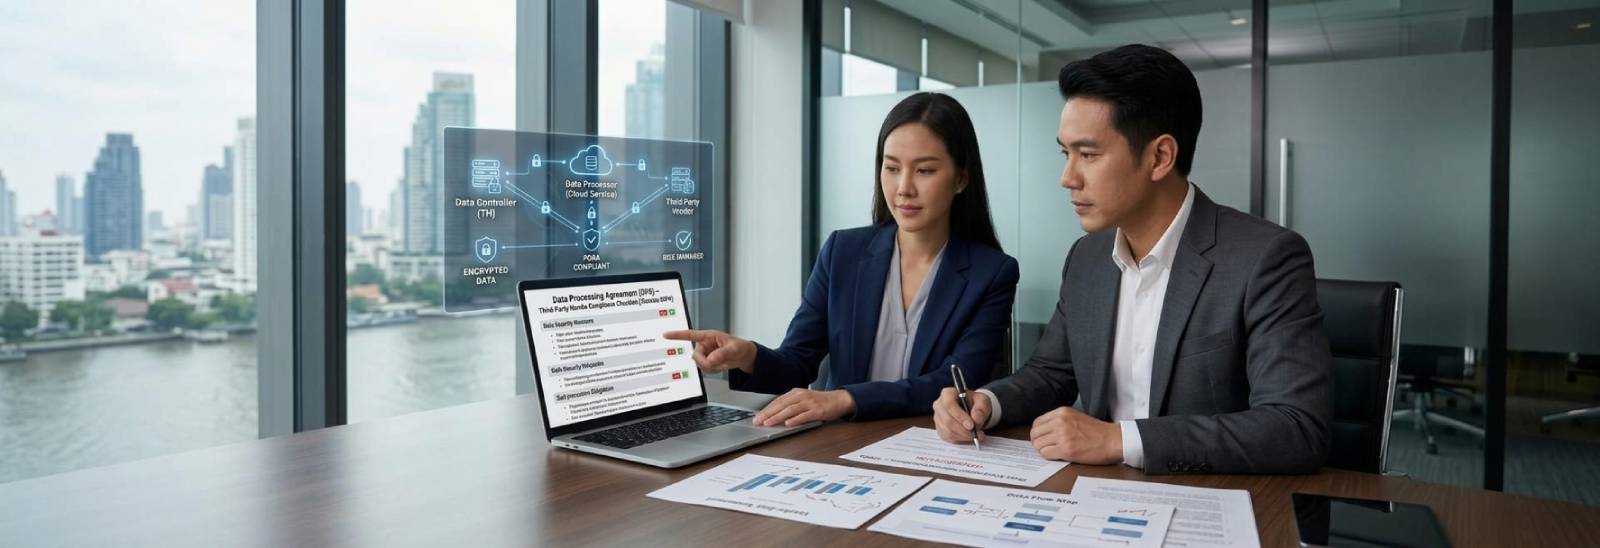
For many years, organizations treated data protection obligations as a peripheral contractual issue, often addressed through a brief confidentiality or privacy provision buried within a Master Services Agreement. That approach is increasingly incompatible with Thailand's evolving regulatory environment.
As enforcement of the Personal Data Protection Act B.E. 2562 (2019) (PDPA) continues to mature, regulators are placing greater emphasis on demonstrable accountability rather than mere policy declarations. The legal question is no longer whether an organization has included a privacy clause in its commercial agreement, but whether it can evidence a robust governance framework governing the collection, use, disclosure, storage, transfer, and protection of personal data throughout its operational ecosystem.
In practice, most organizations now rely extensively on third-party service providers to perform critical business functions. Cloud hosting providers, payroll processors, HR platforms, customer relationship management systems, marketing agencies, data analytics firms, and outsourced support centers routinely access substantial volumes of personal data on behalf of businesses. Each of these relationships creates a distinct legal and compliance risk profile that cannot be adequately addressed through generic contractual language.
A standalone Data Processing Agreement (DPA) has therefore emerged as an essential governance instrument, establishing a clear allocation of responsibilities between data controllers and data processors while creating a contractual framework capable of withstanding regulatory scrutiny.
The Regulatory Imperative of Lawful Basis Governance
One of the most significant developments under the PDPA is the increasing expectation that organizations maintain a comprehensive understanding of the legal basis supporting every processing activity involving personal data.
Many organizations have invested considerable effort in updating privacy notices and consent mechanisms, yet comparatively few have ensured that these legal foundations are consistently reflected throughout their vendor management framework. This disconnect often becomes apparent during regulatory investigations, where organizations are required to demonstrate not only that a lawful basis exists, but also that it has been operationalized across all processing arrangements.
A sophisticated DPA should therefore extend beyond a generic description of services and establish a detailed governance structure addressing the categories of personal data involved, the purposes of processing, applicable lawful bases, retention obligations, security requirements, and restrictions on further use or disclosure. Where personal data is transferred outside Thailand, the agreement should further articulate the safeguards implemented to ensure compliance with cross-border transfer requirements.
This level of contractual precision serves a broader purpose. It enables organizations to demonstrate that personal data governance has been embedded within operational decision-making processes rather than treated as a standalone compliance exercise. In an environment where regulators increasingly assess accountability through evidence of governance maturity, such documentation can become a critical component of an organization's defensive strategy.
Data Breach Preparedness and the Expanding Scope of Vendor Risk
Cybersecurity incidents have fundamentally altered the way organizations evaluate third-party relationships. While businesses traditionally focused on service quality, pricing, and operational efficiency during vendor selection, data protection obligations now demand a far more comprehensive assessment of risk.
A significant proportion of modern data breaches originate within third-party environments, creating complex challenges for organizations that remain legally accountable for personal data processed on their behalf. Under the PDPA, data controllers are subject to stringent notification obligations and may be required to report qualifying incidents to regulators within a compressed timeframe. Delays in obtaining information from a processor can therefore create regulatory exposure independent of the underlying breach itself.
For this reason, breach response provisions have become one of the most strategically important elements of a DPA. Organizations increasingly require contractual mechanisms that guarantee immediate notification of security incidents, unrestricted cooperation during investigations, access to relevant forensic information, and clearly defined responsibilities throughout the incident response process.
The objective is not merely regulatory compliance. Effective breach provisions ensure that organizations maintain operational control during a crisis, preserve their ability to satisfy statutory reporting obligations, and reduce the likelihood that a processor's failure will escalate into a broader legal or reputational event.
As cyber threats continue to evolve in sophistication and frequency, DPAs are increasingly functioning as extensions of an organization's cybersecurity governance framework rather than traditional legal appendices.
The Commercial Significance of Liability Allocation
Perhaps the most commercially consequential aspect of a modern DPA lies in its treatment of liability.
Historically, privacy provisions were often negotiated as secondary issues within broader commercial agreements. That position has changed dramatically. Data breaches, regulatory investigations, and privacy-related litigation now represent material financial risks capable of generating losses that significantly exceed the value of the underlying service contract.
Consequently, organizations are devoting increasing attention to the allocation of responsibility for regulatory penalties, remediation costs, third-party claims, cybersecurity investigations, and business interruption losses. Questions concerning liability caps, indemnification obligations, insurance requirements, audit rights, and sub-processor oversight have become central components of commercial negotiations.
This evolution reflects a broader shift in corporate governance. Data protection is no longer viewed solely as a legal compliance matter; it is increasingly recognized as an enterprise risk issue with direct implications for shareholder value, customer trust, and organizational resilience.
The most sophisticated organizations therefore approach DPA negotiations through a risk-based lens. Rather than relying on standardized templates, they calibrate contractual protections according to the sensitivity of the data involved, the scale of processing activities, and the potential consequences of a security or compliance failure.
Conclusion: DPAs as a Cornerstone of Corporate Data Governance
The maturation of Thailand's PDPA has transformed the role of Data Processing Agreements within commercial relationships. What was once regarded as a supplementary contractual document has become a cornerstone of modern data governance.
Organizations are now expected to demonstrate not only that personal data is processed lawfully, but also that appropriate controls exist throughout the entire data lifecycle, including across outsourced functions and third-party service providers. Regulators increasingly evaluate accountability through governance structures, documented decision-making processes, and contractual safeguards that evidence active oversight of data processing activities.
Against this backdrop, a standalone DPA should not be viewed as a compliance formality designed to satisfy regulatory requirements. Rather, it represents a strategic mechanism for managing legal exposure, allocating risk, strengthening cybersecurity preparedness, and enhancing organizational resilience in an increasingly data-driven economy.
For businesses operating in Thailand's evolving regulatory landscape, the question is no longer whether a DPA is necessary. The more relevant question is whether existing contractual arrangements are sufficiently robust to withstand the scrutiny of regulators, customers, investors, and other stakeholders when a data protection incident inevitably occurs.
